Audit Log
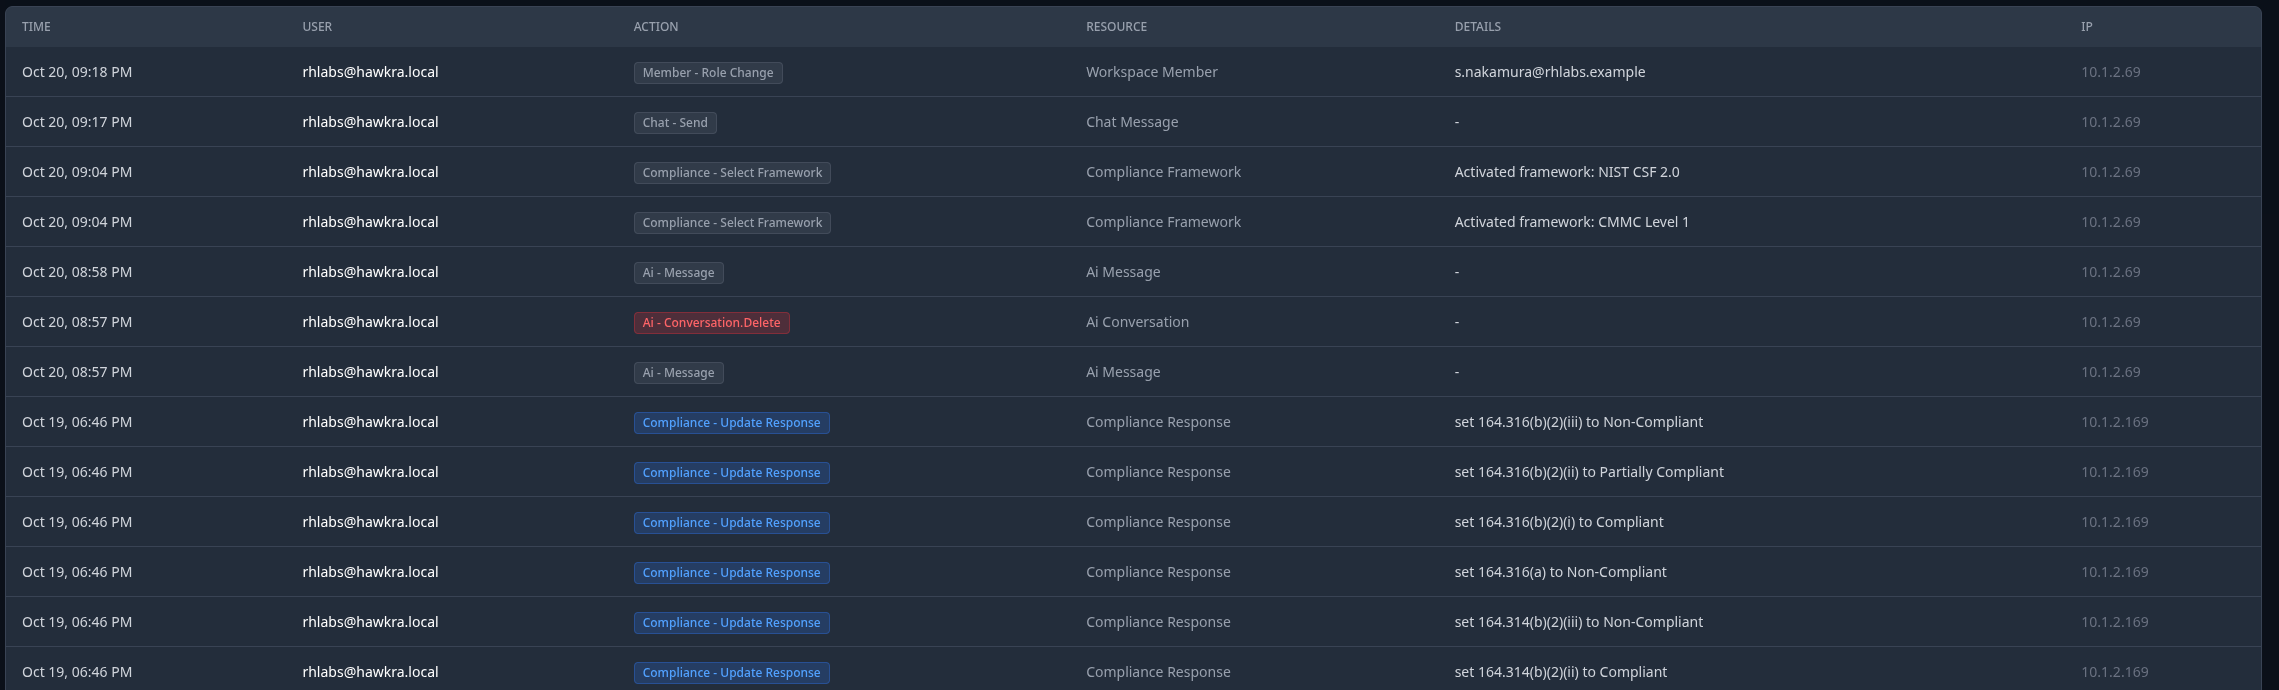
The workspace audit log provides a complete, tamper-evident record of all significant actions taken within a workspace. Every change -- from creating an asset to viewing a credential -- is logged with the user who performed it, the timestamp, and the IP address from which the action originated.
How It Works
Each entry records the acting user, action type, affected resource, timestamp, and source IP address. Audit log entries are append-only at the database level (they cannot be edited or deleted) and are visible to all workspace members. They are kept even after the workspace or the acting user's account is deleted.
What Actions Are Logged
Hawkra logs a comprehensive set of actions across all workspace features:
Workspace Management
workspace.create, workspace.update, workspace.delete, workspace.rotate_encryption_key, dashboard_layout.update
Team and Invitations
invitation.create, invitation.accept, invitation.decline, invitation.cancel, member.role_change, member.remove
Assets, Networks, and Ports
asset.create, asset.update, asset.delete, asset.import_mac_data, network.create, network.update, network.delete, port.create, port.update, port.delete
Vulnerabilities
vulnerability.create, vulnerability.update, vulnerability.delete, vulnerability.created_from_library, vulnerability.saved_to_library, vulnerability.ai_autocomplete, vulnerability_asset.link, vulnerability_asset.unlink, vulnerability_asset.status_change
Sensitive Data Access
credential.view_sensitive, credential.create, credential.update, credential.delete
Scans and Imports
scan.create, scan.cancel, scan.delete, scan.reconnect, scan.discard, import.create
Compliance
compliance.select_framework, compliance.deselect_framework, compliance.update_response, compliance.add_evidence, compliance.delete_evidence
Reports, Exports, and Documents
report.generate, export.assets, export.vulnerabilities, export.compliance, document.create, document.update, document.delete, file.upload, file.delete
Remediation
remediation.assign, remediation.unassign, remediation.comment
Other
note.create, note.update, note.delete, agent.deploy, agent.approve, agent.revoke, agent.delete, agent_task.create, agent_task.cancel, agent_task.delete, ai.message, proof.create, proof.update, proof.delete
Credential views are logged as sensitive access events (credential.view_sensitive). Every time a user decrypts and views a stored credential, it is recorded with their identity and IP address. This provides a clear chain of custody for sensitive data.