Report Builder
The Report Builder generates professional security assessment reports from your workspace data. Reports are scoped to individual networks and include vulnerability summaries, severity distributions, affected hosts, and detailed findings with proof of exploitation. Output is a downloadable DOCX file that can be customized with your branding, client details, and supporting artifacts.
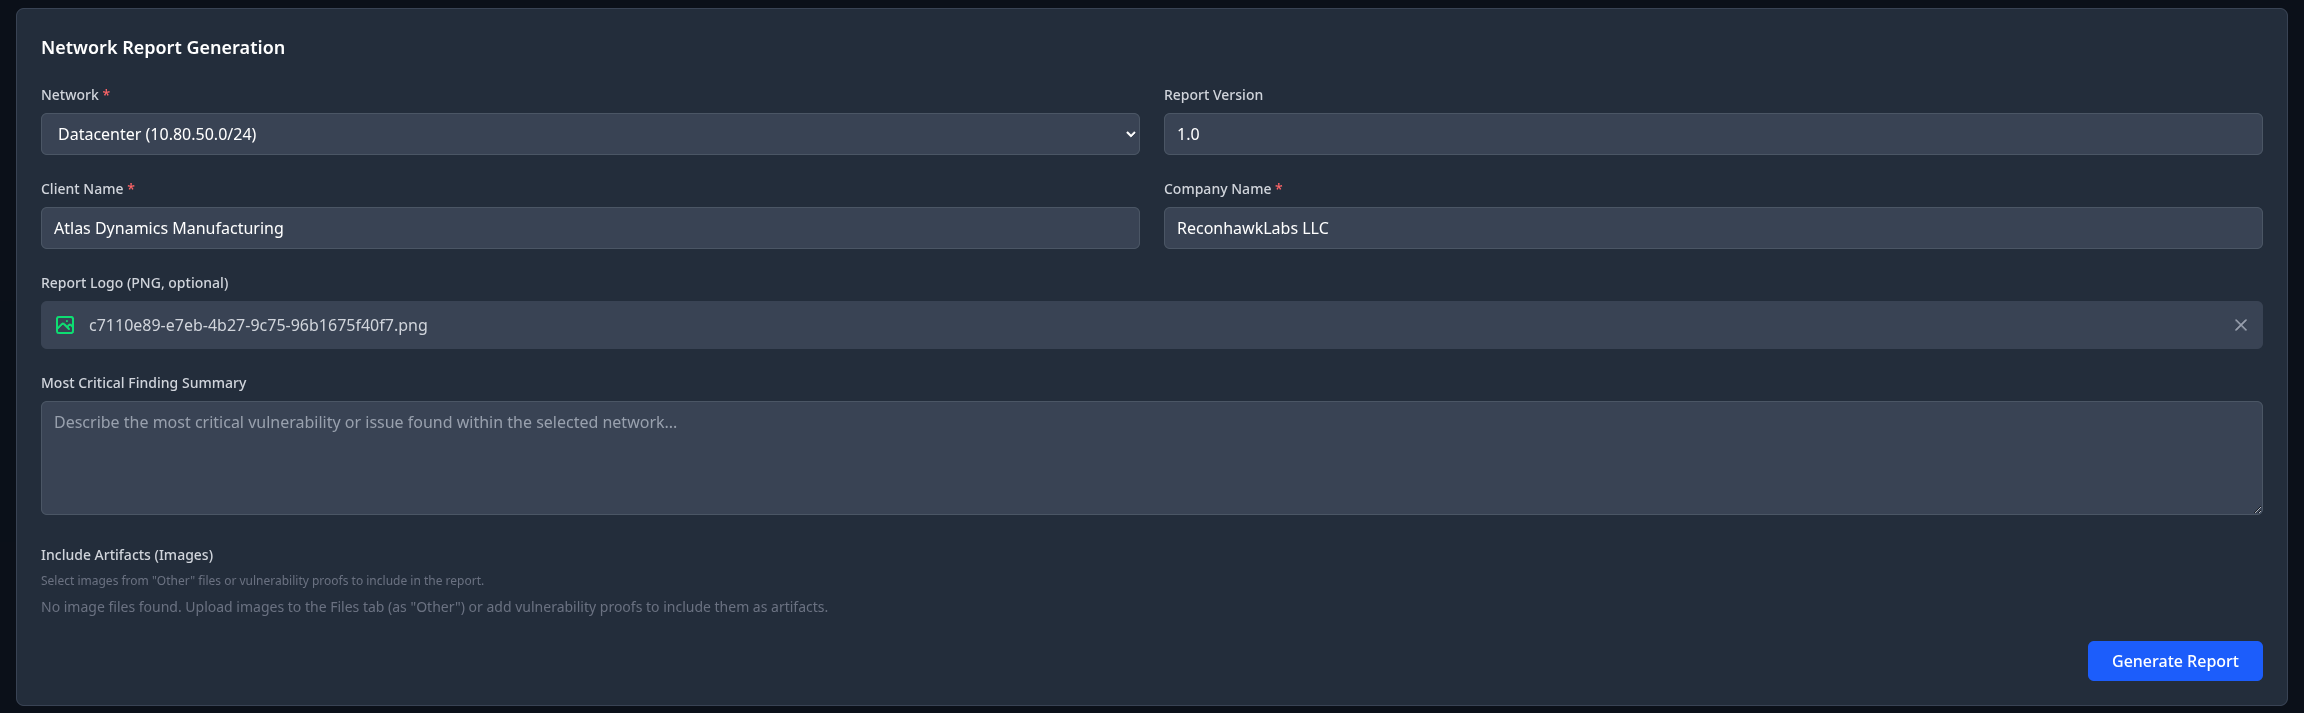
How It Works
Hawkra aggregates all vulnerability data for the selected network and merges it into a DOCX template. Encrypted notes and proof data are decrypted transparently during generation.
Report Contents
A generated report includes the following sections:
- Cover Page -- Client name, company name, version, date.
- Vulnerability Summary -- Counts by severity, most common vulnerabilities.
- Severity Distribution -- Breakdown across severity levels.
- Affected Hosts -- All assets with IPs, hostnames, MACs, descriptions.
- Detailed Findings -- Each vulnerability with CVE/CWE, severity, description, affected hosts/ports, proof, and recommended fixes.
- Artifact Appendix -- Attached evidence images.
Sorted by severity (Critical first), then by affected host count.
Customization Options
Required Fields
| Field | Description |
|---|---|
| Client Name | The name of the client receiving the report (max 255 characters). |
| Company Name | Your company or team name for the report header (max 255 characters). |
Optional Fields
| Field | Description |
|---|---|
| Report Version | A version string for the report, such as "1.0" or "Draft" (default: "1.0", max 50 characters). |
| Critical Finding Summary | A free-text executive summary highlighting the most critical findings (max 10,000 characters). |
Custom Logo
Upload your company logo to brand the report. The logo must be an image file (PNG, JPEG, etc.) and is placed on the cover page. Upload the logo file to your workspace first, then reference it during report generation.
Custom report logos require a Premium subscription. Free-tier users can generate reports without custom branding.
Artifact Attachments
You can attach supporting evidence to the report as artifacts. These can be:
- Documents -- Files uploaded to your workspace's document library (category "Other").
- Proofs -- Screenshots and evidence files attached to specific vulnerability-asset associations.
Only image files (PNG, JPEG, etc.) are included in the generated report. Non-image artifacts are skipped. Each artifact appears in the report with its name and description.
Generating a Report
- Navigate to your workspace and select the network you want to report on.
- Open the Report section.
- Fill in the Client Name and Company Name.
- Optionally set the Report Version and write a Critical Finding Summary.
- Optionally upload and select a custom logo.
- Optionally attach artifact files for supporting evidence.
- Click Generate Report.
- The report is generated server-side and returned as a downloadable DOCX file.
Downloading Reports
Once generation completes, the report downloads automatically. The filename follows the pattern:
{NetworkName}_Network_Report_{YYYYMMDD}.docx
For example: Production_LAN_Network_Report_20260303.docx
Report Limits
Report generation is subject to tier-based monthly limits:
| Tier | Monthly Reports |
|---|---|
| Free | 3 per month |
| Premium | Unlimited |
| Self-Hosted | Unlimited |
When you reach your monthly limit, Hawkra displays a message indicating how many reports you have used and suggests upgrading for unlimited access.