Remediation Tracking
Remediation Tracking provides a structured workflow for managing vulnerability fixes from discovery through resolution. Each vulnerability-asset association in your workspace is a remediation item that can be assigned to team members, tracked through status changes, documented with proof of remediation, and discussed through collaborative comments. All remediation notes are encrypted at rest.
Remediation tracking is available to Premium and Self-Hosted users.
How It Works
Each vulnerability-asset pair in your workspace becomes a remediation link -- an individually trackable task with status workflow, assignment, and full audit trail.
Status Workflow
A remediation link carries the status of its vulnerability-asset link, which progresses through three states:
Identified --> Validated --> Remediated
| Status | Meaning |
|---|---|
| Identified | The vulnerability has been documented on this asset but not yet confirmed. |
| Validated | The vulnerability has been confirmed on this asset. |
| Remediated | The vulnerability has been fixed and verified on this asset. |
The remediation list groups links as Open (Identified or Validated) and Remediated. Status is changed from the vulnerability's detail view; see Vulnerabilities.
A link marked Remediated can no longer be assigned. Make sure the fix is verified before marking it as remediated.
Listing and Filtering
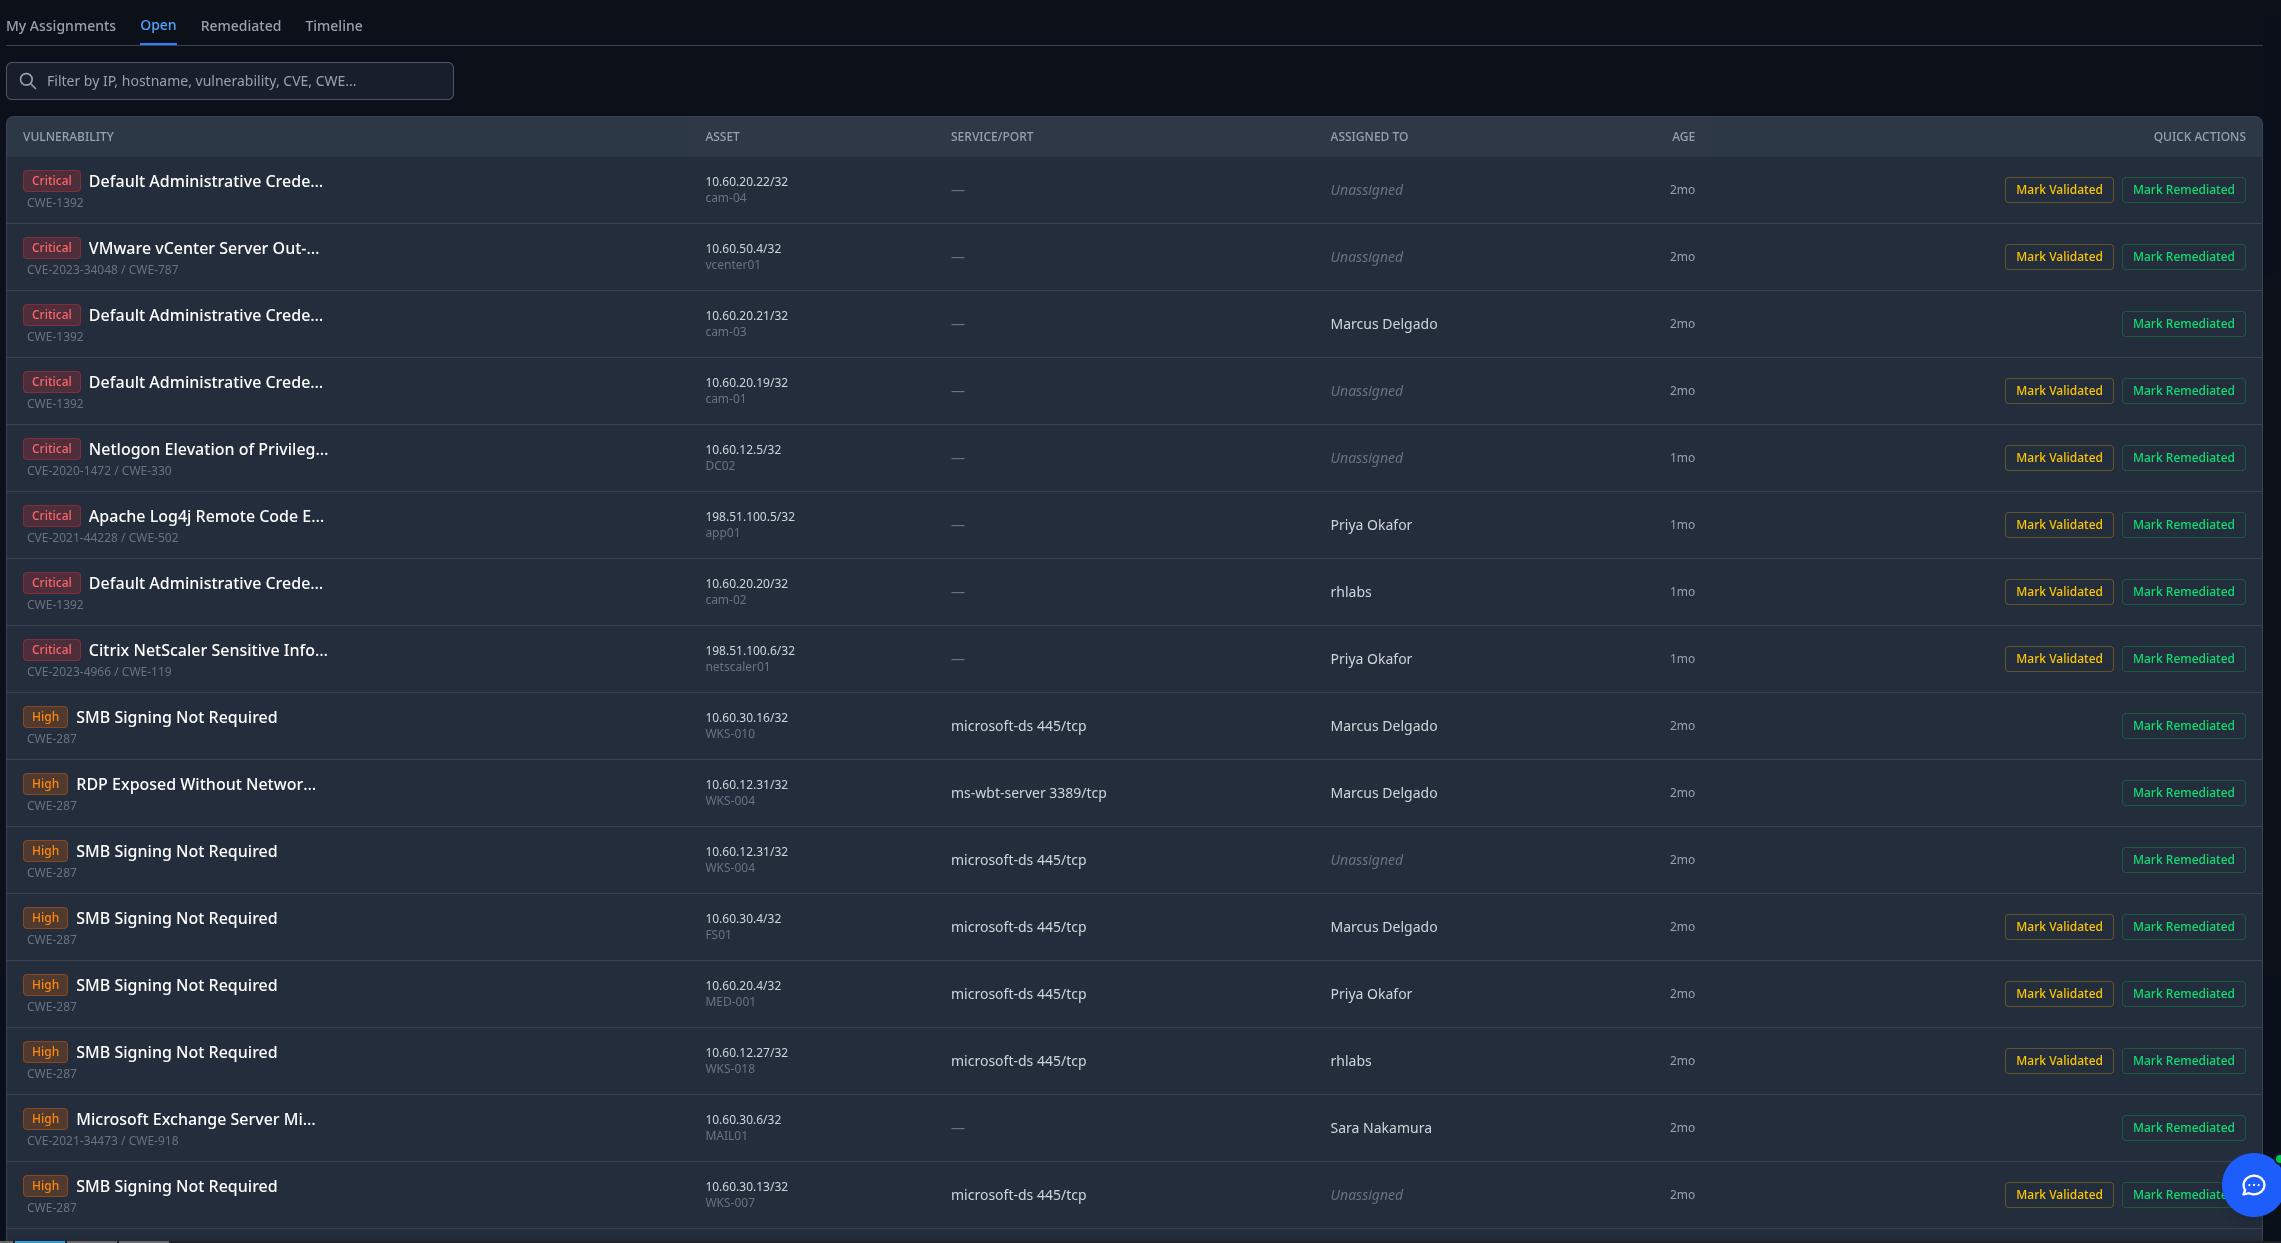
The remediation view shows all vulnerability-asset links in your workspace with filtering and search capabilities:
Available Filters
| Filter | Options | Description |
|---|---|---|
| Status | Open, Remediated | Show links that are not yet remediated, or only remediated ones. |
| Assigned To | Any workspace member, or "Me" | Show only links assigned to a specific user. Use "Me" to see your own assignments. |
| Search | Free text | Search across vulnerability names, asset IP addresses, and hostnames. |
Results are paginated with configurable page sizes (1 to 100 items per page, default 50).
Link Information
Each remediation link in the list shows:
- Vulnerability -- Name, severity, CVSS score, CVE, and CWE identifiers.
- Asset -- IP address and hostname of the affected system.
- Port -- Port number, protocol, and service name (if the vulnerability is port-specific).
- Status -- Current remediation state.
- Assigned To -- The team member responsible, with their display name and email.
- Notes -- Encrypted remediation notes (decrypted for display).
Assigning Remediation Tasks
Assigning a Link
To assign a remediation link to a team member:
- Open the remediation link detail view.
- Select a workspace member to assign.
- The link must not already be assigned (unassign first if reassigning).
Only workspace members with the Owner, Editor, or Remediation Analyst role can be assigned remediation tasks.
Unassigning
To reassign a link, first unassign the current member, then assign the new one. Both actions are recorded in the remediation timeline.
Who Can Assign
Assigning and unassigning requires the EditVulnerabilities permission.
Remediation Details
Clicking on a remediation link opens a detailed view with:
- Vulnerability details -- Full description, severity, CVSS score, CVE/CWE identifiers, reference links, recommended fixes, and impact assessment.
- Asset details -- IP address, hostname, operating system, OS version, and the network the asset belongs to.
- Port details -- Port number, protocol, service name, and service version (if applicable).
- Proofs -- Evidence files attached to the vulnerability-asset association (screenshots, logs, etc.).
- Comments -- A threaded discussion for the remediation team.
Proof of Remediation
Attach evidence files to document that a vulnerability has been remediated. Proofs are linked to the specific vulnerability-asset association and are visible in both the remediation detail view and in generated reports.
Comments
Remediation links support collaborative comments for team communication:
- Any workspace member with EditVulnerabilities permission can add comments.
- Comments are limited to 5,000 characters each.
- Each comment records the author and timestamp.
- Comments appear in chronological order in the detail view.
Comments are useful for documenting remediation decisions, requesting additional information, or recording the steps taken to fix a vulnerability.
Timeline
The remediation timeline provides a chronological audit trail of all activity across your workspace's remediation links. Each event records:
- Who performed the action (user display name).
- What happened (assignment, status change, comment added).
- When it happened.
- Which vulnerability and asset were involved.
Timeline Filters
| Filter | Description |
|---|---|
| Vulnerability ID | Show events for a specific vulnerability. |
| Asset ID | Show events for a specific asset. |
| Event Type | Filter by event type (assigned, unassigned, status_changed, comment_added). |
| Date Range | Show events within a specific date window. |
The timeline is paginated and supports the same page size controls as the remediation list.
Encrypted Notes
Remediation notes associated with each vulnerability-asset link are encrypted using your workspace's data encryption key (DEK). Notes are encrypted before storage and decrypted only when viewed by an authorized workspace member. This ensures sensitive remediation details remain protected at rest.