Access Control
The Access Control category manages authentication and authorization settings that control how users register and verify their accounts on your Hawkra instance.
Settings Reference
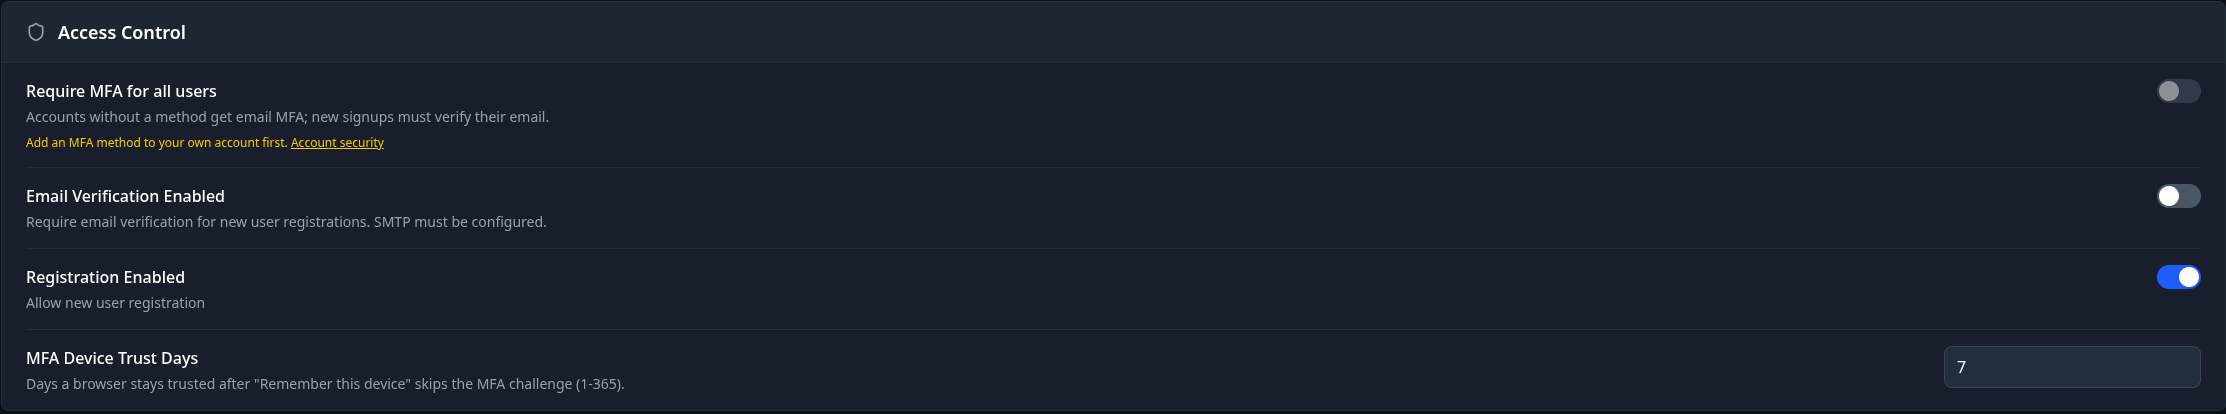
Registration Enabled
| Key | registration_enabled |
| Type | Boolean (toggle) |
| Default | false (since 1.1.3) |
Controls whether new users can create accounts on your instance through the public registration page. When enabled, anyone with access to your Hawkra URL can register a new account (subject to any license-imposed user limits). It is off by default on self-hosted instances since 1.1.3 (an instance whose admin had already turned it on keeps it on); with it off, admins create accounts from the admin area. Only verified accounts count toward the licensed user limit, and registrations that are never verified are removed after 24 hours.
Require MFA for All Users
| Key | mfa_required |
| Type | Boolean |
| Default | false |
When enabled, every account must use multi-factor authentication. Accounts that have no MFA method are given email MFA and must enter a code sent to their email address at their next login; new registrations must verify their email address before the account is active; users cannot remove their last MFA method.
Prerequisites: the administrator turning this on must already have an MFA method on their own account, and SMTP must be configured (restart after changing SMTP settings). The toggle stays disabled until both are true. When you enable it, Hawkra shows how many accounts currently have no MFA method — any of those that cannot receive email at their address will be unable to log in.
Environment override: MFA_REQUIRED=true (or false) forces the value and makes the toggle read-only. Any other value stops Hawkra from starting.
First-run setup: set MFA_REQUIRED (or turn the setting on) only after the initial administrator account has a real email address or a TOTP method. While first-run setup is incomplete the requirement is not applied at login, so the bootstrap administrator can sign in and finish setup.
Email Verification Enabled
| Key | email_verification_enabled |
| Type | Boolean (toggle) |
| Default | false |
When enabled, newly registered users must verify their email address by entering a 6-character verification code sent to the email they registered with. Until the code is entered, the account is not fully activated. Registering the same address again while it is still unverified replaces the pending registration: the newest registration's password is the one that applies, codes issued for earlier attempts stop working, and a new code is emailed unless one was sent within the last minute (in which case the code already in the mailbox still applies).
Prerequisites: SMTP must be configured before enabling this setting. If SMTP is not set up, the verification emails cannot be sent and users will be unable to complete registration.
When disabled:
- Users are activated immediately upon registration without any email verification step.
Enabling email verification without a working SMTP configuration will prevent new users from completing registration. Configure and test your SMTP settings before turning this on.
Configuration via Environment Variables
| Setting | Environment Variable |
|---|---|
| Registration Enabled | REGISTRATION_ENABLED |
| Email Verification Enabled | EMAIL_VERIFICATION_ENABLED |
| Require MFA for All Users | MFA_REQUIRED |
| Global API Rate Limit (requests/min) | API_RATE_LIMIT_PER_MINUTE |
The global API rate limit defaults to 500 requests per minute and is keyed by the access-token hash for authenticated requests (so each user gets their own budget even when many users share the same reverse-proxy IP), falling back to client IP for unauthenticated requests. Set API_RATE_LIMIT_PER_MINUTE=0 to disable the global limit — useful when Hawkra sits behind another reverse proxy or WAF that already enforces rate limiting. Per-route limits on authentication, token refresh, MFA, agent protocol, OSINT, and exports always apply regardless of this setting.
Remember that your license defines the maximum number of users allowed on the instance. Even with registration enabled, new registrations will be rejected once the user limit is reached. The registration page will display a "Registration Unavailable" message in this case.